Roles vs. Groups: Assigning Roles and Module-Level Access
Last updated: October 17, 2026
Hadrius separates access into two concepts: roles (called "permissions profiles" in the app) and groups. A permissions profile bundles module-level access, such as the ability to submit marketing materials for review, and gives that access to everyone who holds it. Groups are used to organize employees. This article walks through creating a permissions profile, turning on a module-level permission, and assigning the profile to an employee. Do this when a team needs access to a specific part of the platform.
Open Permissions and groups
Start in the People Directory and open Permissions and groups. This is where access is organized for the whole team. Roles and groups serve different purposes, so begin on the permissions side, where you can view, modify and create permissions profiles for your company.
Note: You need the "Manage permissions profiles" permission to create or change a profile. If you don't hold it, the related controls are disabled.
Create a permissions profile
- Select New permissions profile.
- Enter a name that reflects its purpose, such as a marketing review team. A clear name makes the profile easy to find later.
- Select Create permissions profile. Permissions are configured after creation, so the profile starts without any access.
Choose what the profile allows
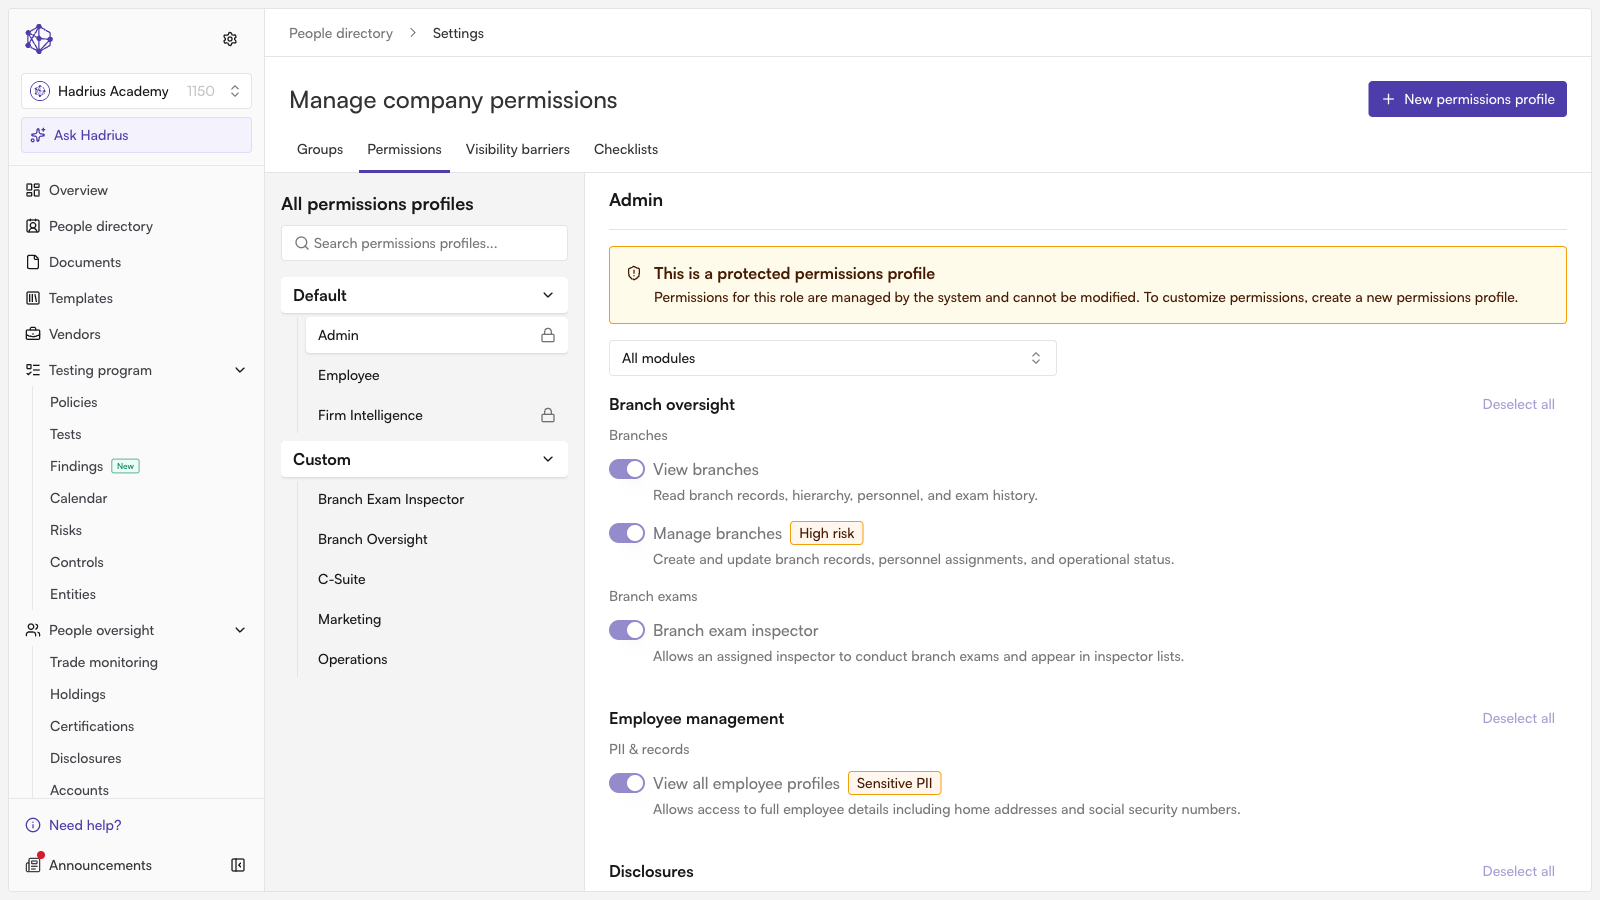
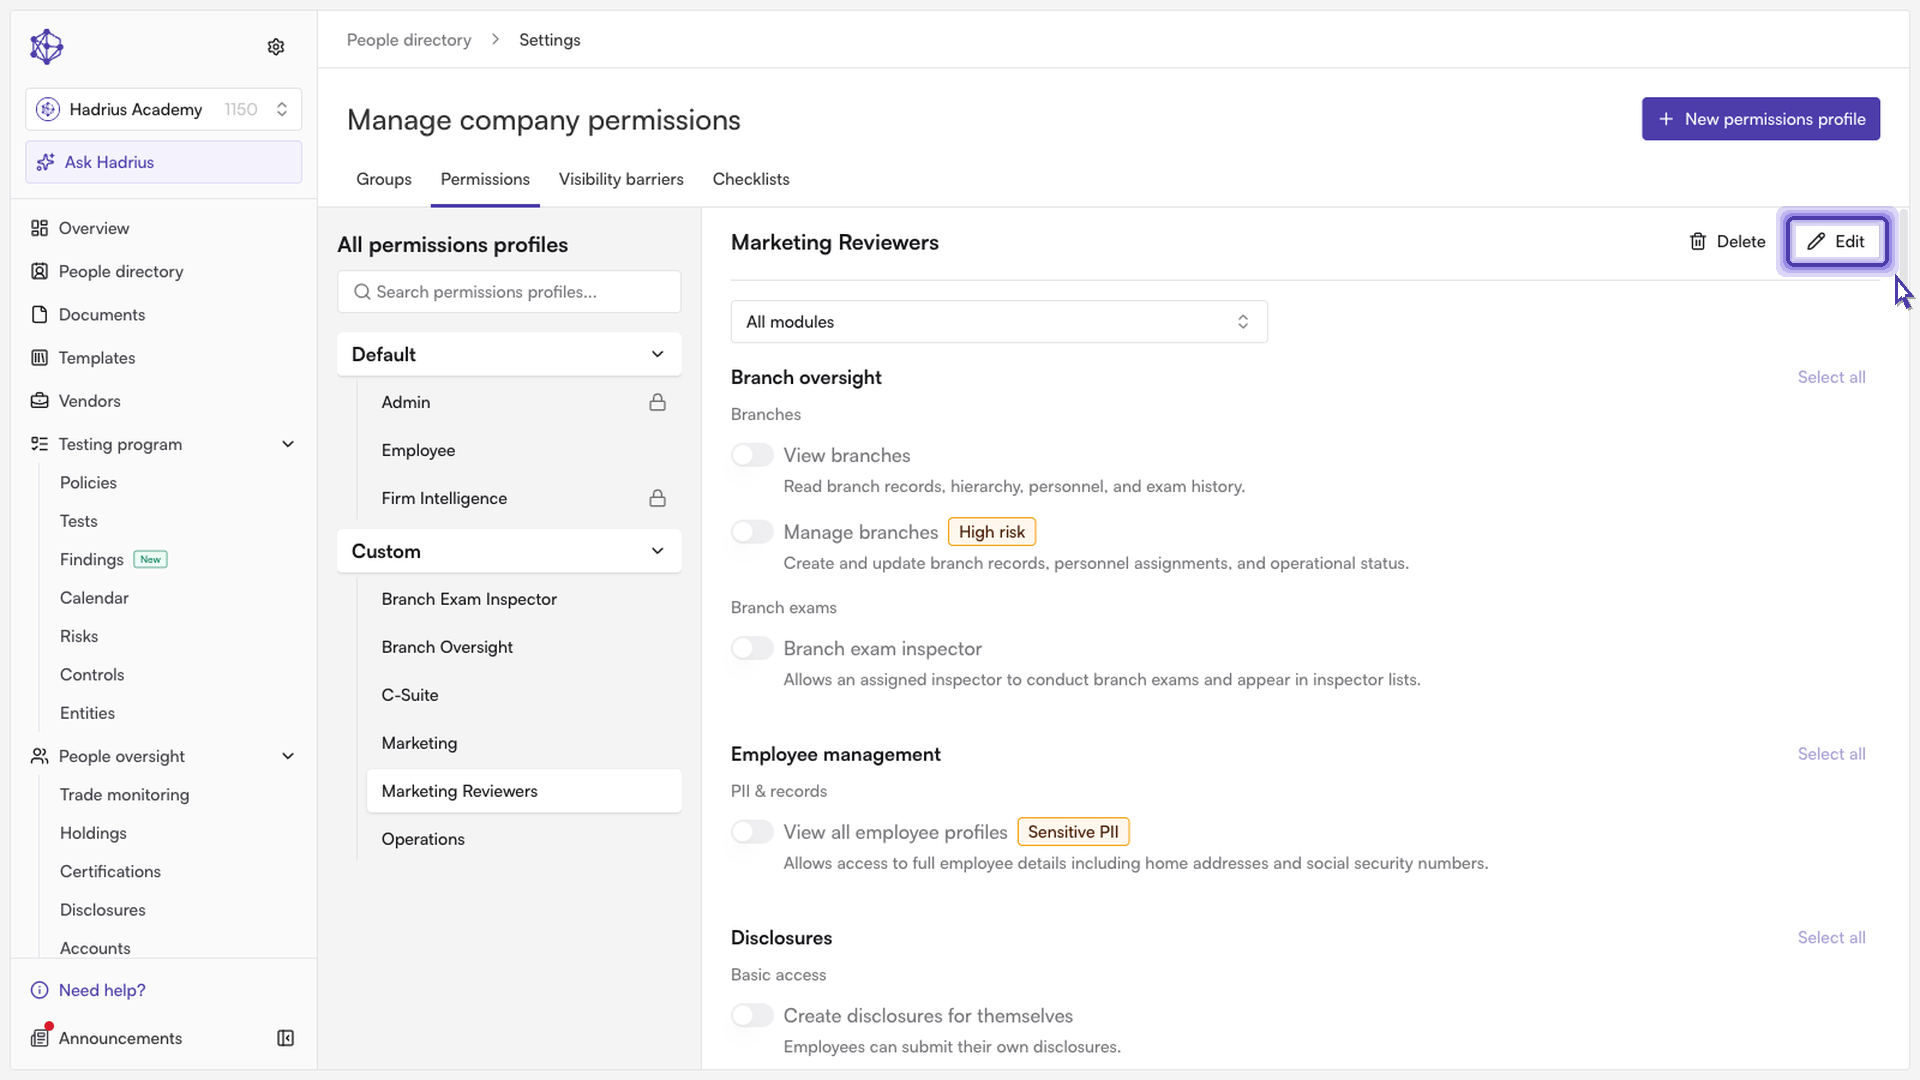
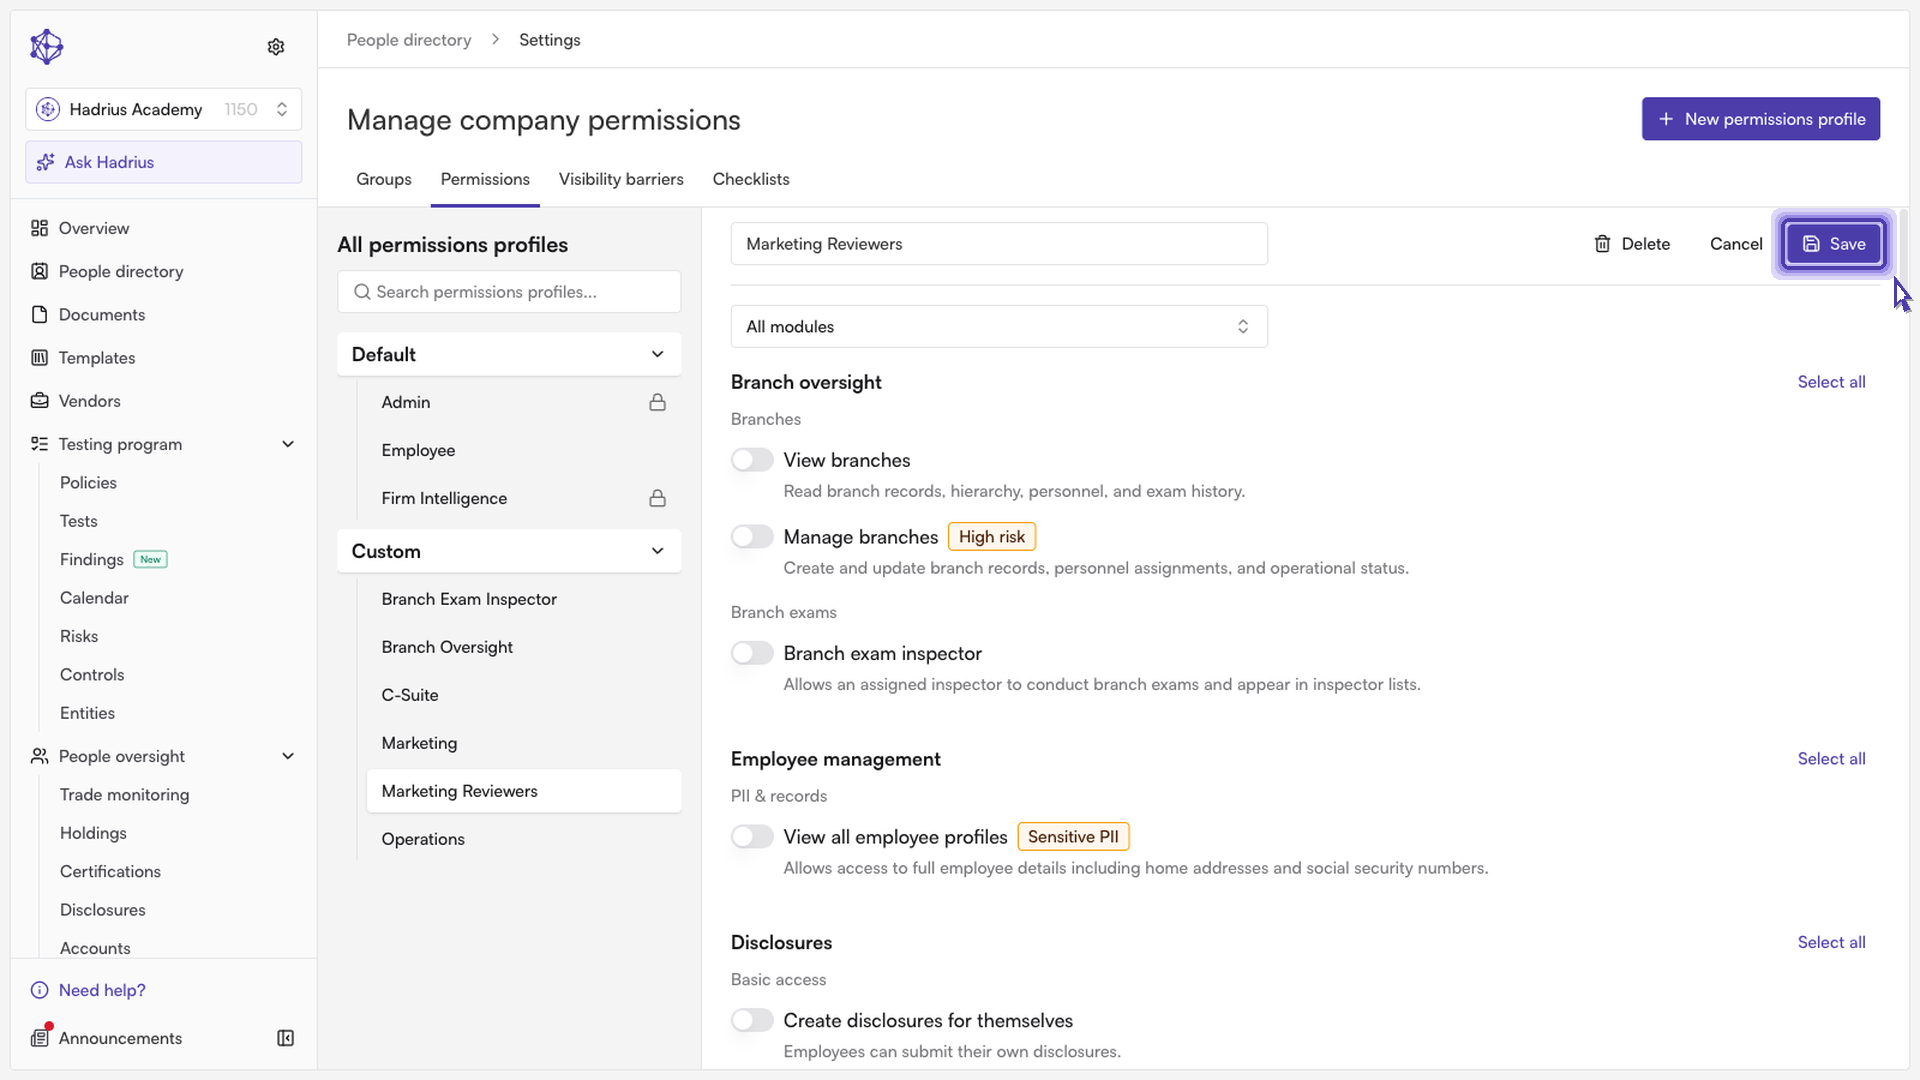
Select the new profile from the sidebar to open it. Then turn on the permissions it should grant. For this example, enable the ability to submit marketing materials for review. Save your changes; anyone who holds this role will receive that access.
Protected profiles are managed by the system and their permissions can't be edited. To customize access, create a new profile instead.
Add members to the profile
A profile only has an effect once people hold it. Open the profile's membership settings and follow these steps:
- Select Add members.
- Choose the employee who should receive this access.
- Confirm to add them.
What happens next
Once confirmed, the employee picks up the profile's module-level permissions right away. To change who holds the profile later, return to its membership settings. You can also remove a direct grant there. Note that anyone who also holds the profile through an audience rule keeps it until that audience is changed.
Groups work differently. A group that holds the members of a permissions profile can't be edited on its own. Manage those members on the profile itself.