How to create a new surveillance rule from a template
Last updated: October 17, 2026
Hadrius includes a library of pre-built surveillance rule templates designed around industry-standard compliance detection logic. Using a template allows your compliance team to rapidly deploy account monitoring rules without building logic from scratch, while retaining full control over detection thresholds, escalation workflows, and account scoping.
Step 1: Access the Rule Library
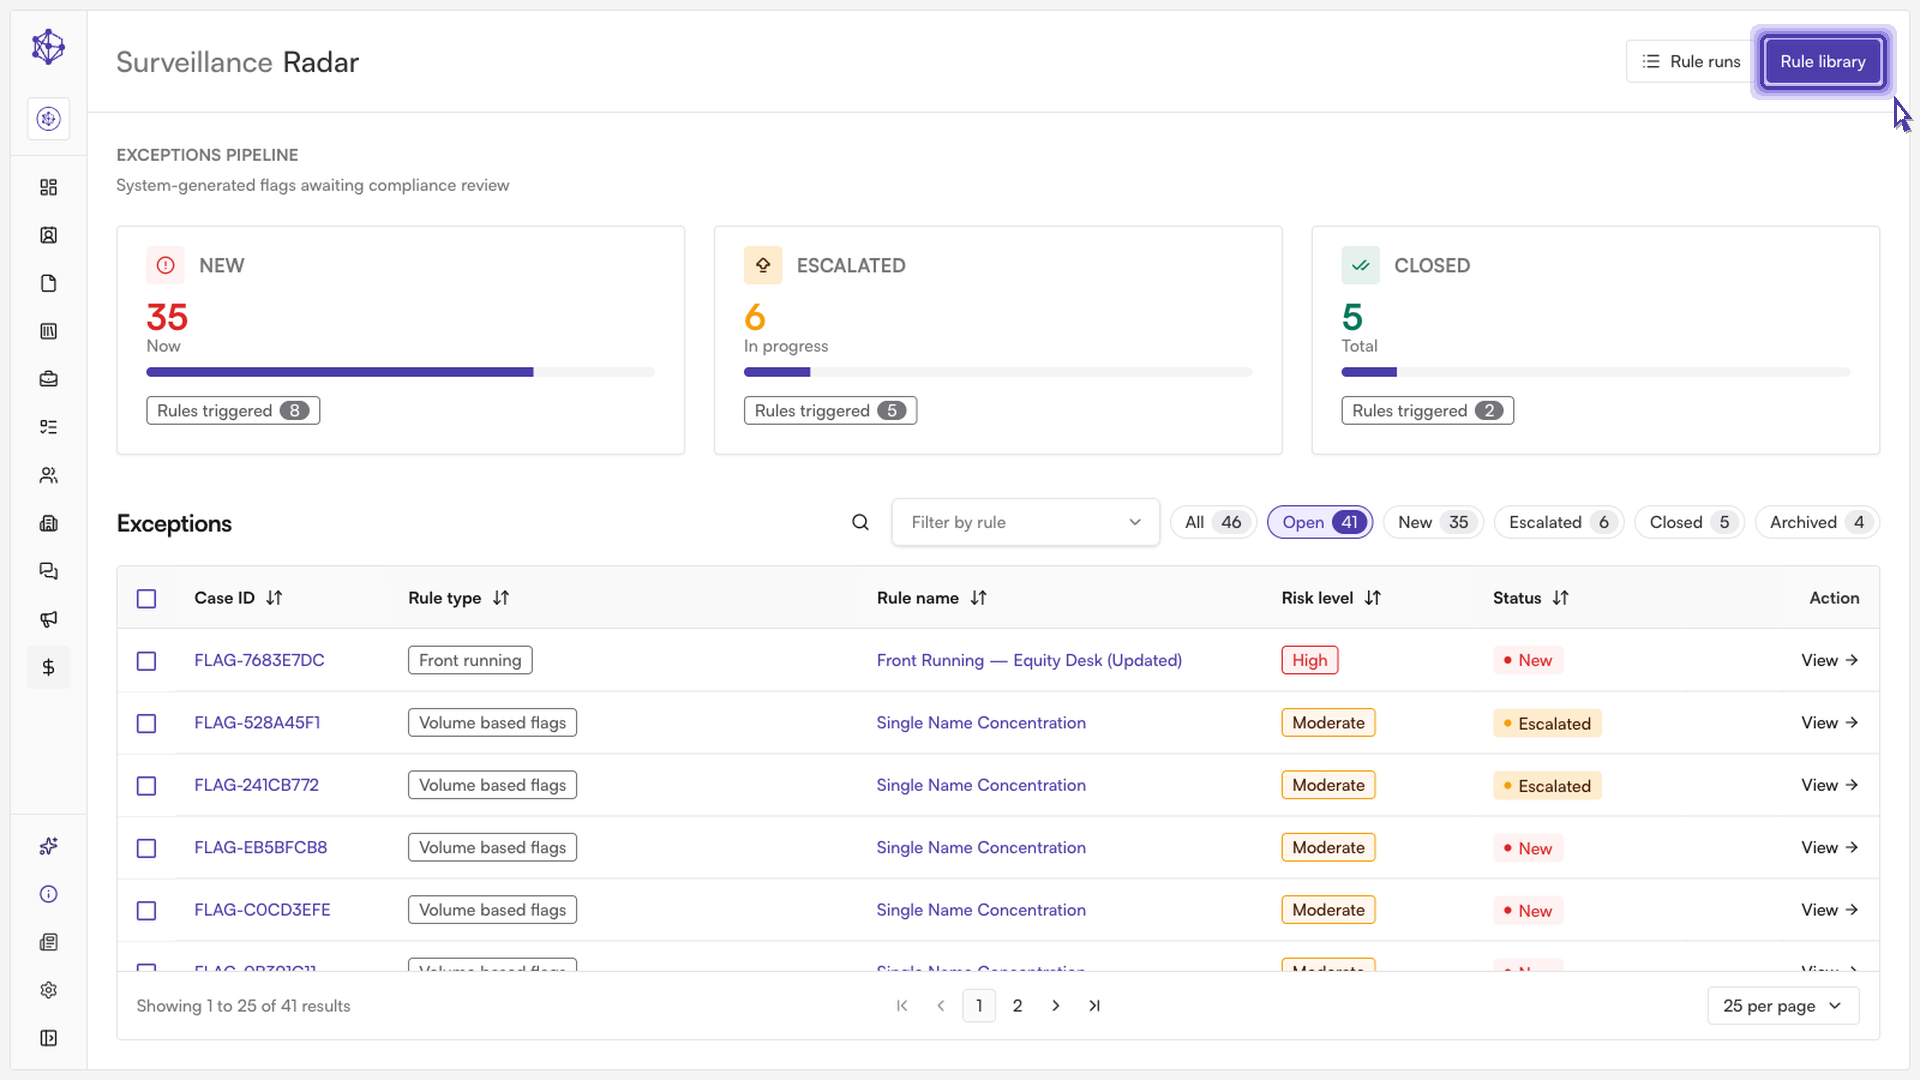
To begin, navigate to Account Surveillance from the main Hadrius navigation bar, then select Rule Library to browse available surveillance options.
Step 2: Choose a Pre-Built Template
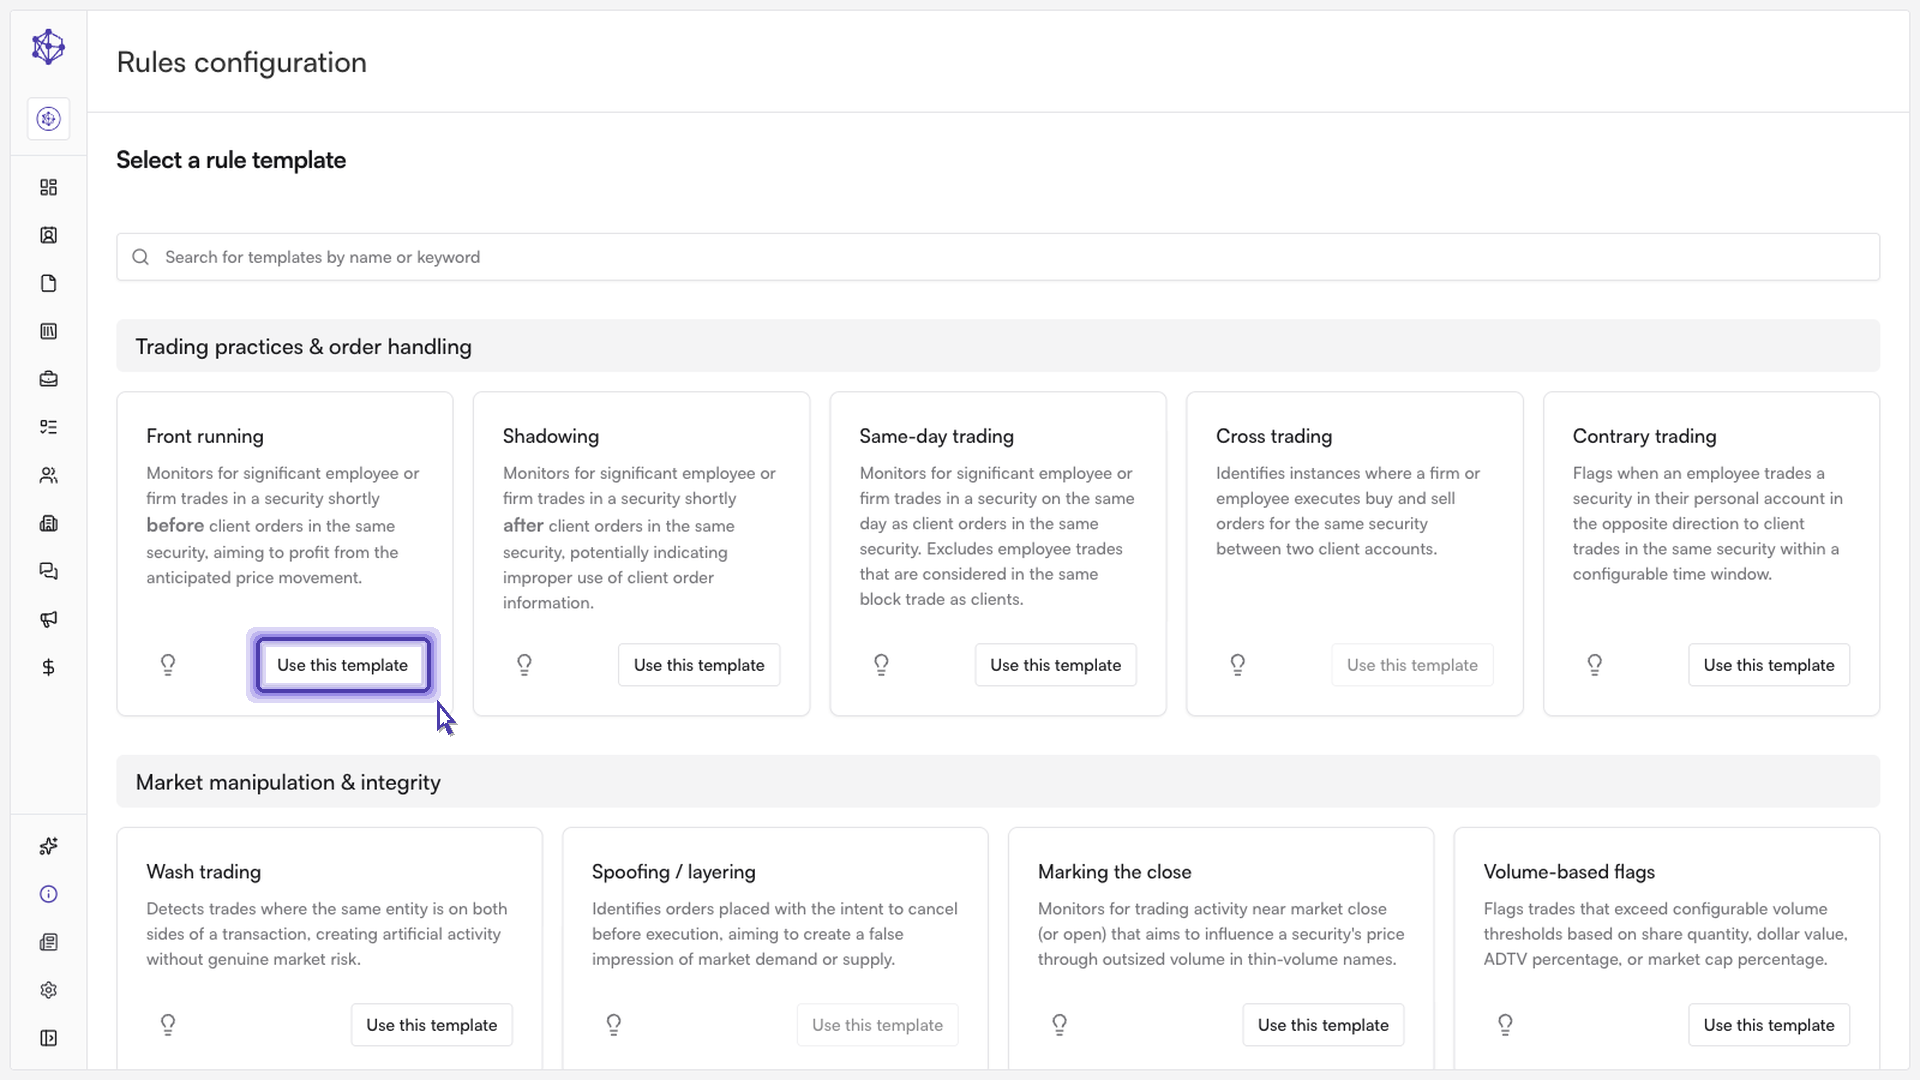
Click New Rule to initiate rule creation. Browse the pre-built templates to find the detection logic suited to your compliance requirements, such as insider trading detection, wash sales, or anomalous activity patterns. Select the template you want to deploy.
Step 3: Define Rule Details and Detection Logic
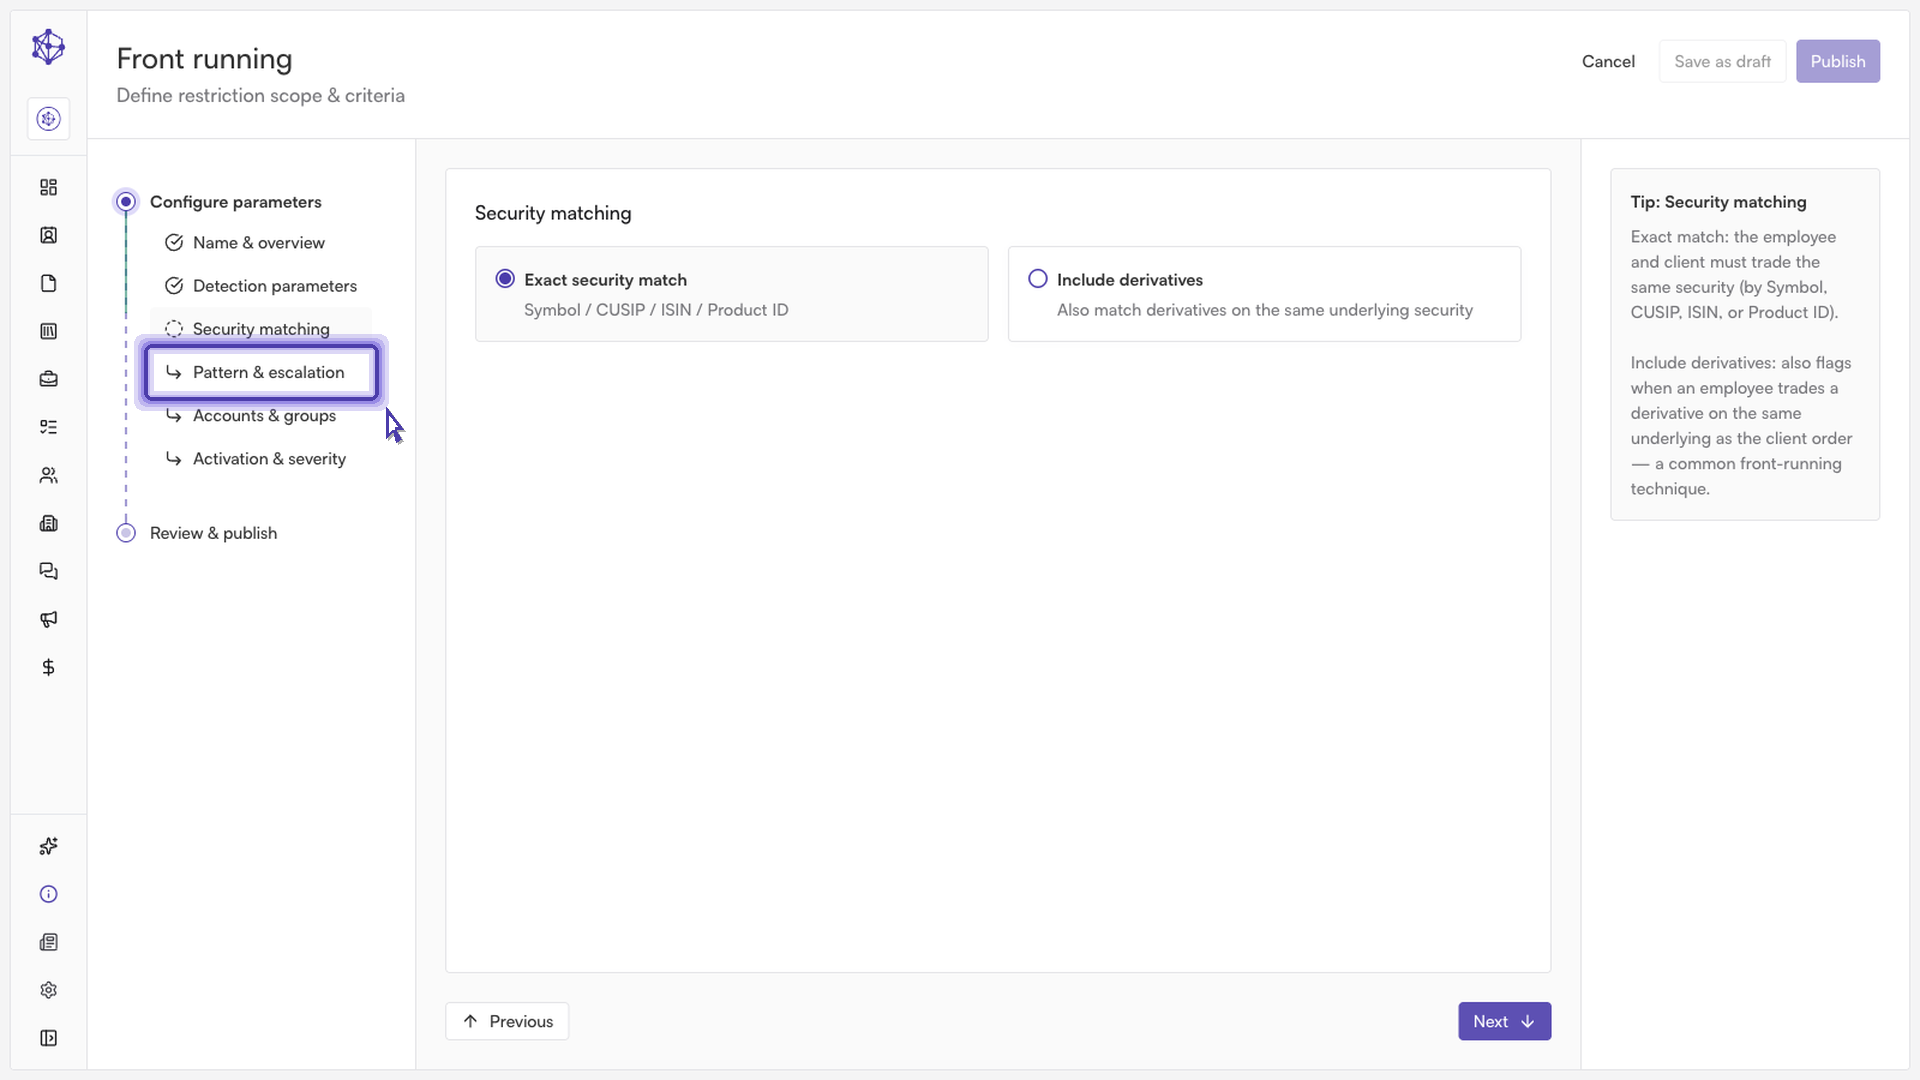
Give your rule a clear, descriptive name so team members can easily identify its monitoring scope across audit logs and alert summaries. Next, fine-tune the template's underlying detection parameters, thresholds, and designated escalation pathways to align with your firm's Written Supervisory Procedures (WSPs).
Step 4: Target Account Groups and Assign Severity
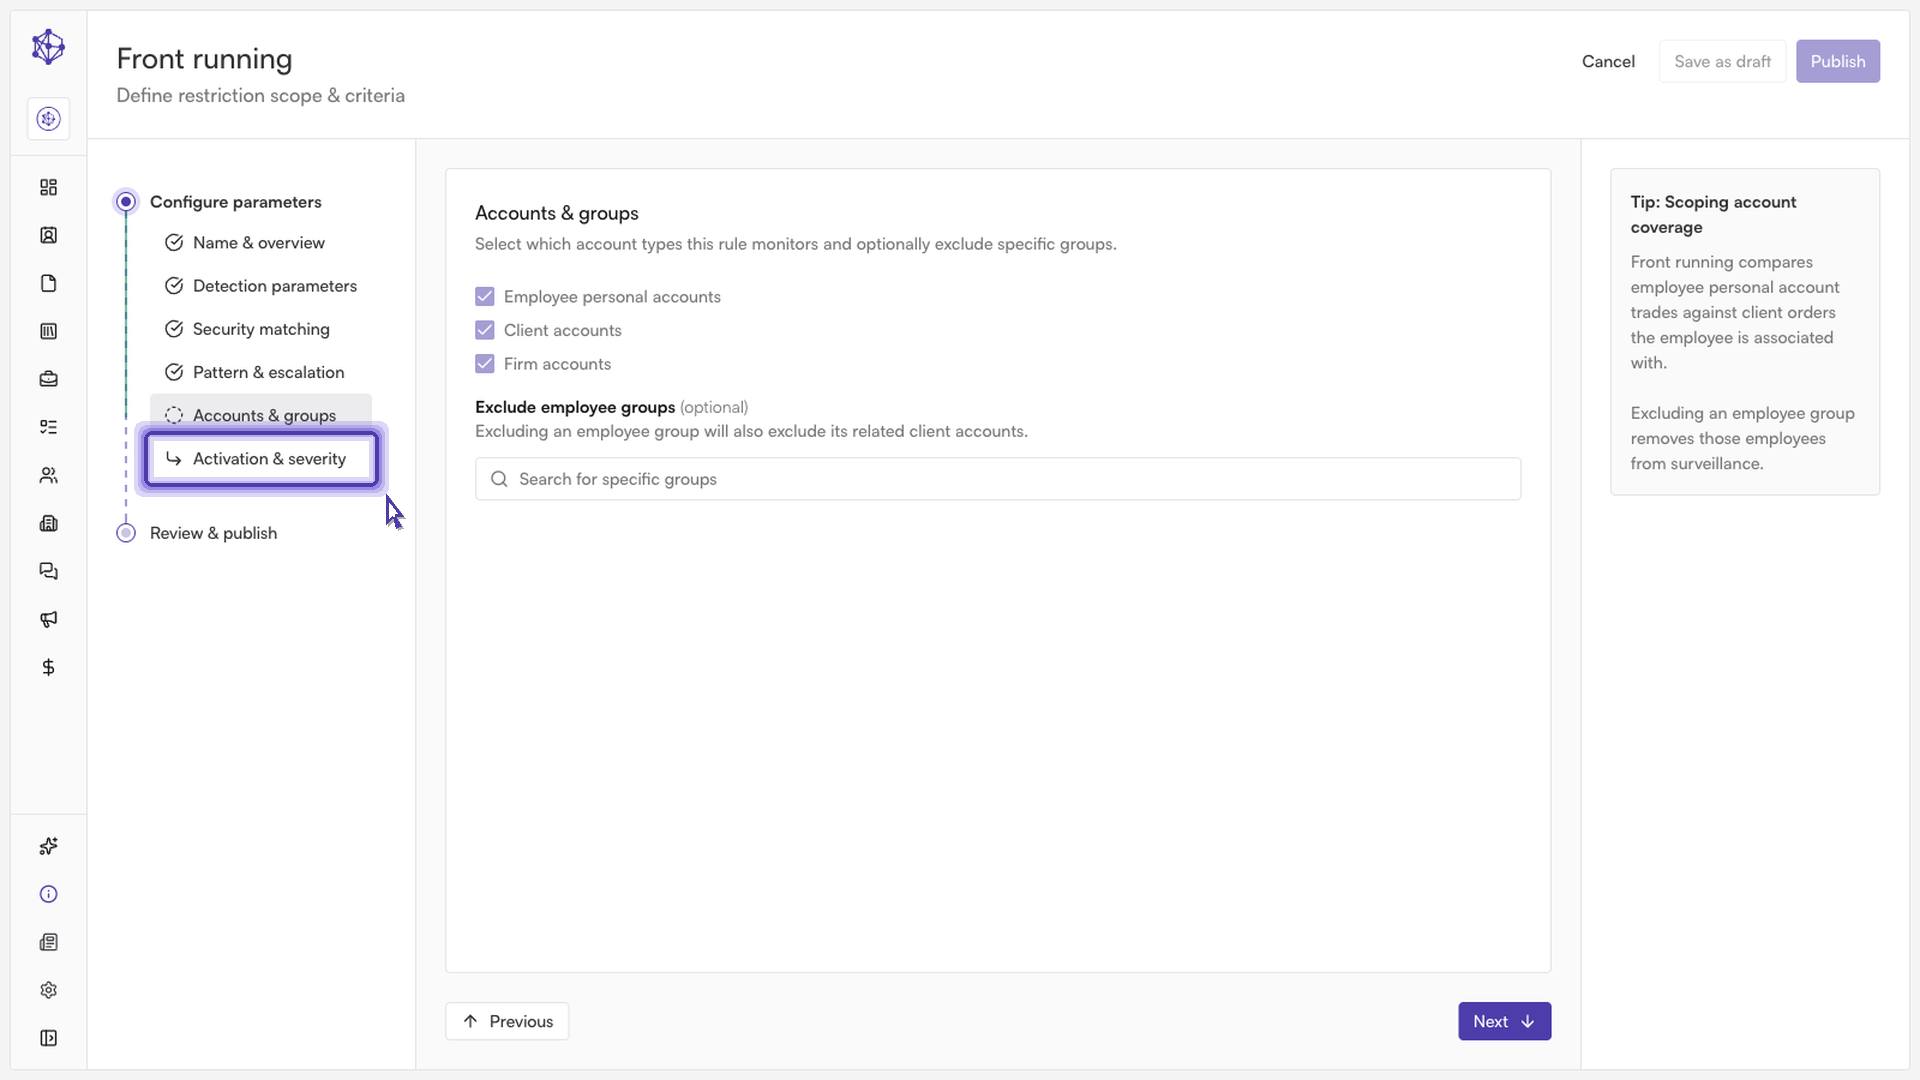
Specify which accounts or employee groups this rule will actively monitor. You can apply the rule firm-wide or restrict it to high-risk groups, specific trading desks, or registered persons. Set an alert severity level (such as Low, Medium, or High) to ensure proper prioritization when potential violations trigger.
Step 5: Review and Publish
Perform a final review of your rule summary to confirm that the detection settings, account groups, and alert parameters match your compliance expectations. When you are ready, click Publish.
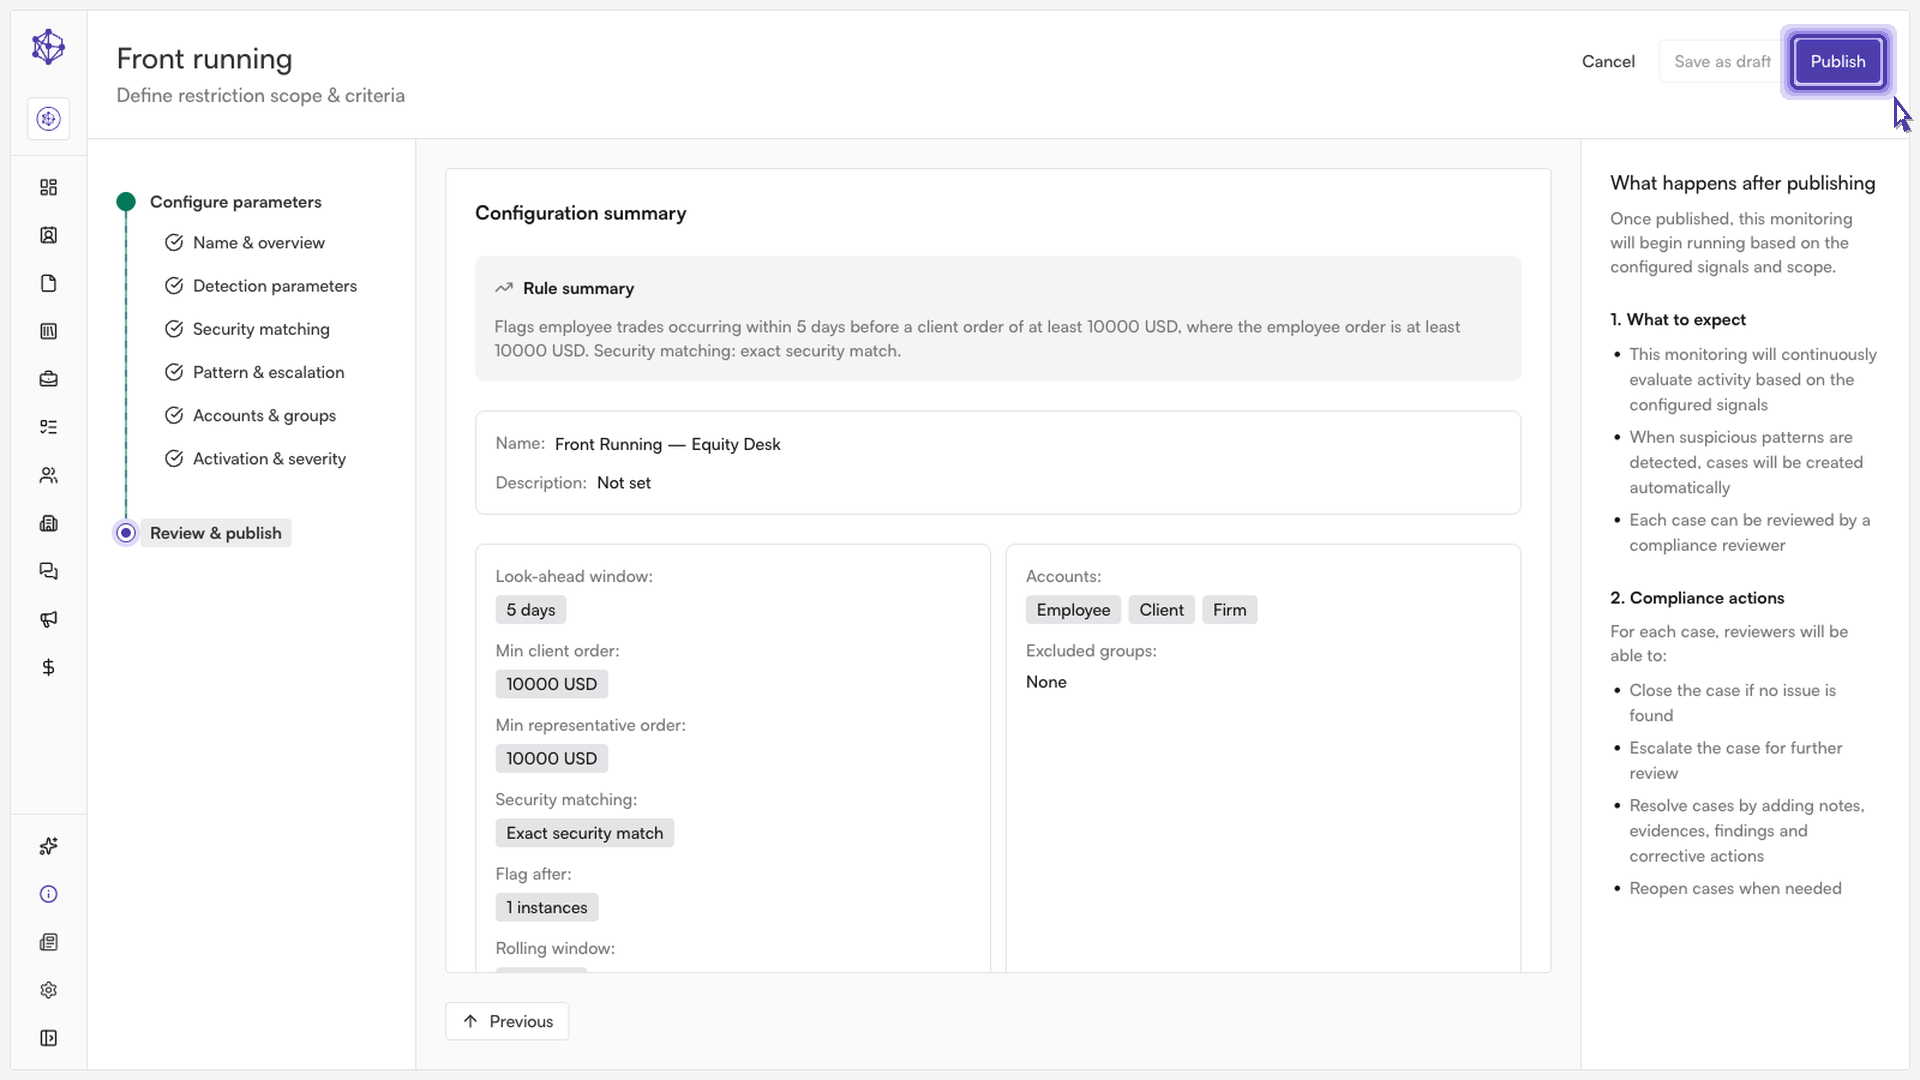
Next Steps: Once published, the rule activates immediately and begins monitoring account activity around the clock. Any triggered events will appear in your Account Surveillance alert queue according to the severity and escalation pathways you configured.