
How do I configure Okta OIDC SSO?
At a glance
Typical setup time: About 15 minutes
Who you need: An Okta administrator
What Hadrius reads: Each user's Okta profile at sign-in
Before you begin
You need administrator access to the Okta Admin Console with permission to create app integrations.
Create an OIDC app integration
In the Okta Admin Console, go to Applications in the left navigation and create a new app integration.
Under Sign-in method, select OIDC - OpenID Connect.
Under Application type, select Web Application.
Configure the app settings
Name
Set App integration name to Hadrius. If you'd like a logo, contact the Hadrius team and we'll send you a high-resolution file.
Grant types
Under Core grants, select both Authorization Code and Refresh Token.
Redirect URIs
Set both Sign-in redirect URIs and Sign-out redirect URIs to:https://app.hadrius.com/auth/sso
Assign users
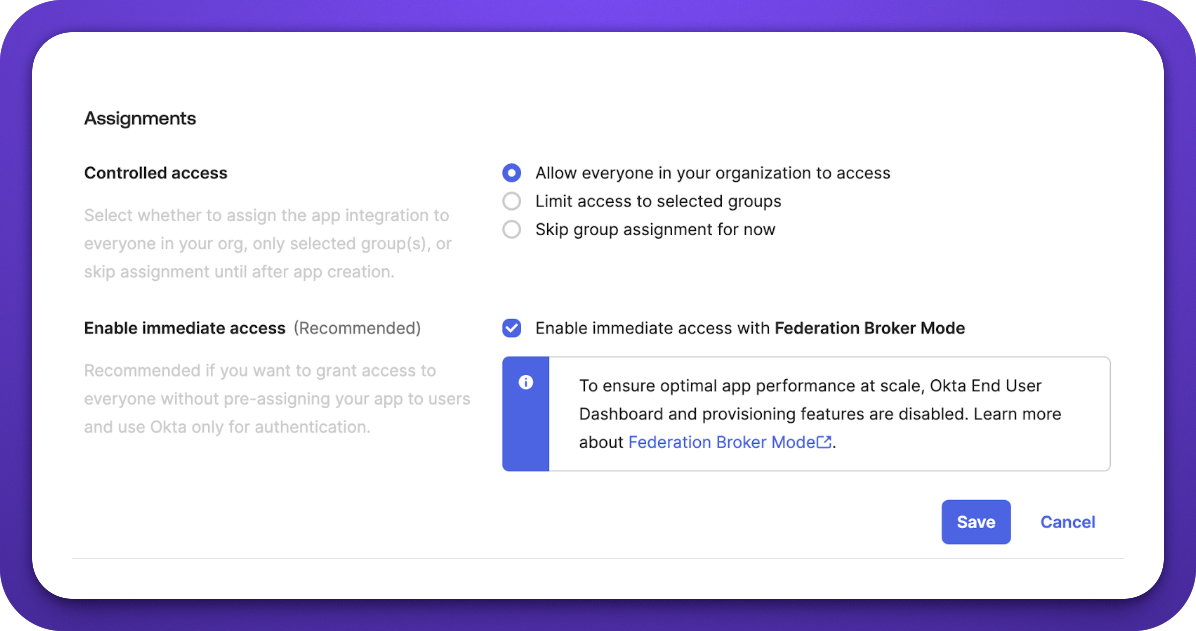
Under Assignments, choose who can sign in to Hadrius with Okta. For example, you can allow everyone in your organization.
Grant the profile scope
On the Okta API Scopes tab, grant okta.myAccount.profile.read so Hadrius can read profile information.
Set a static Issuer URL
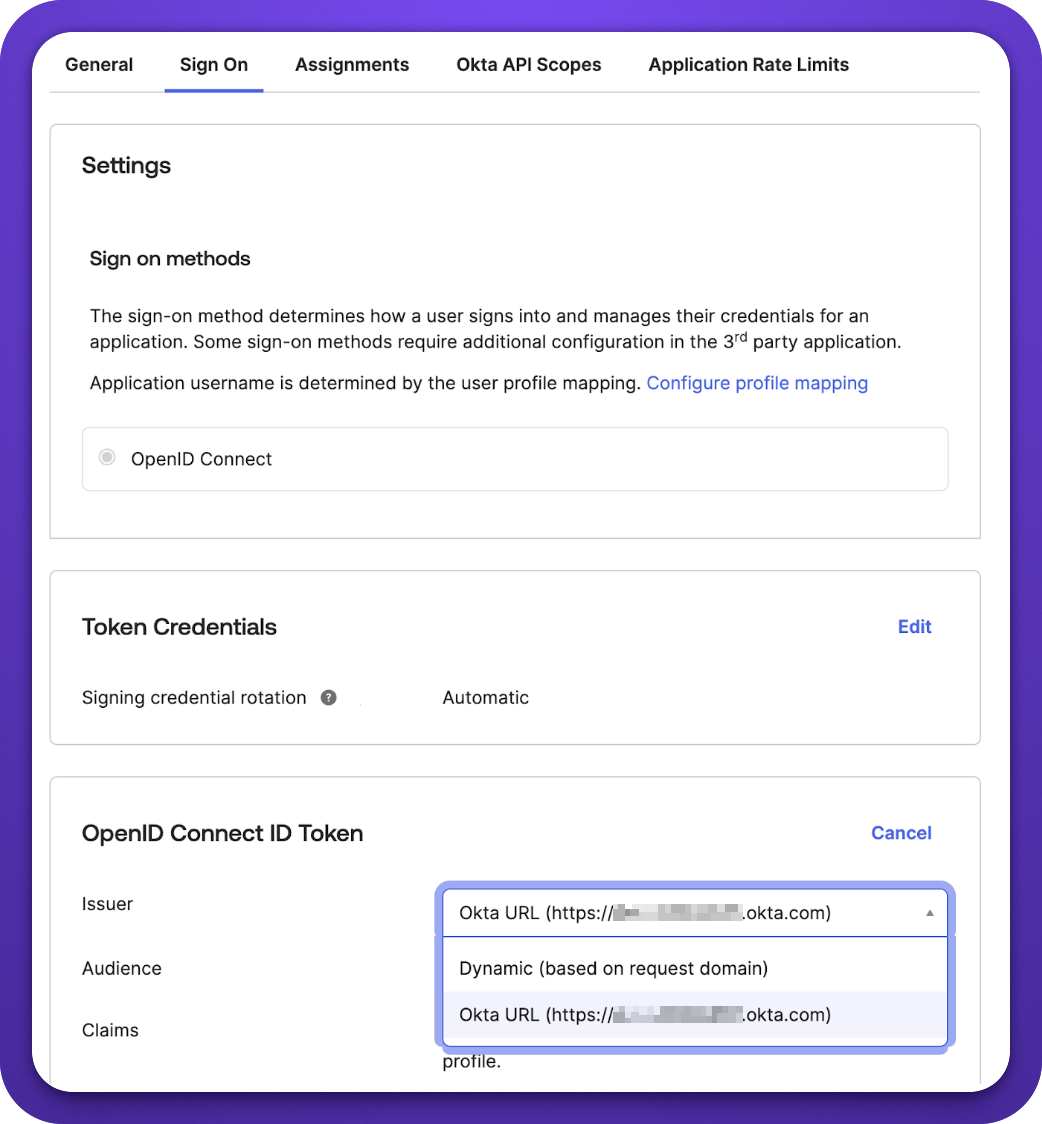
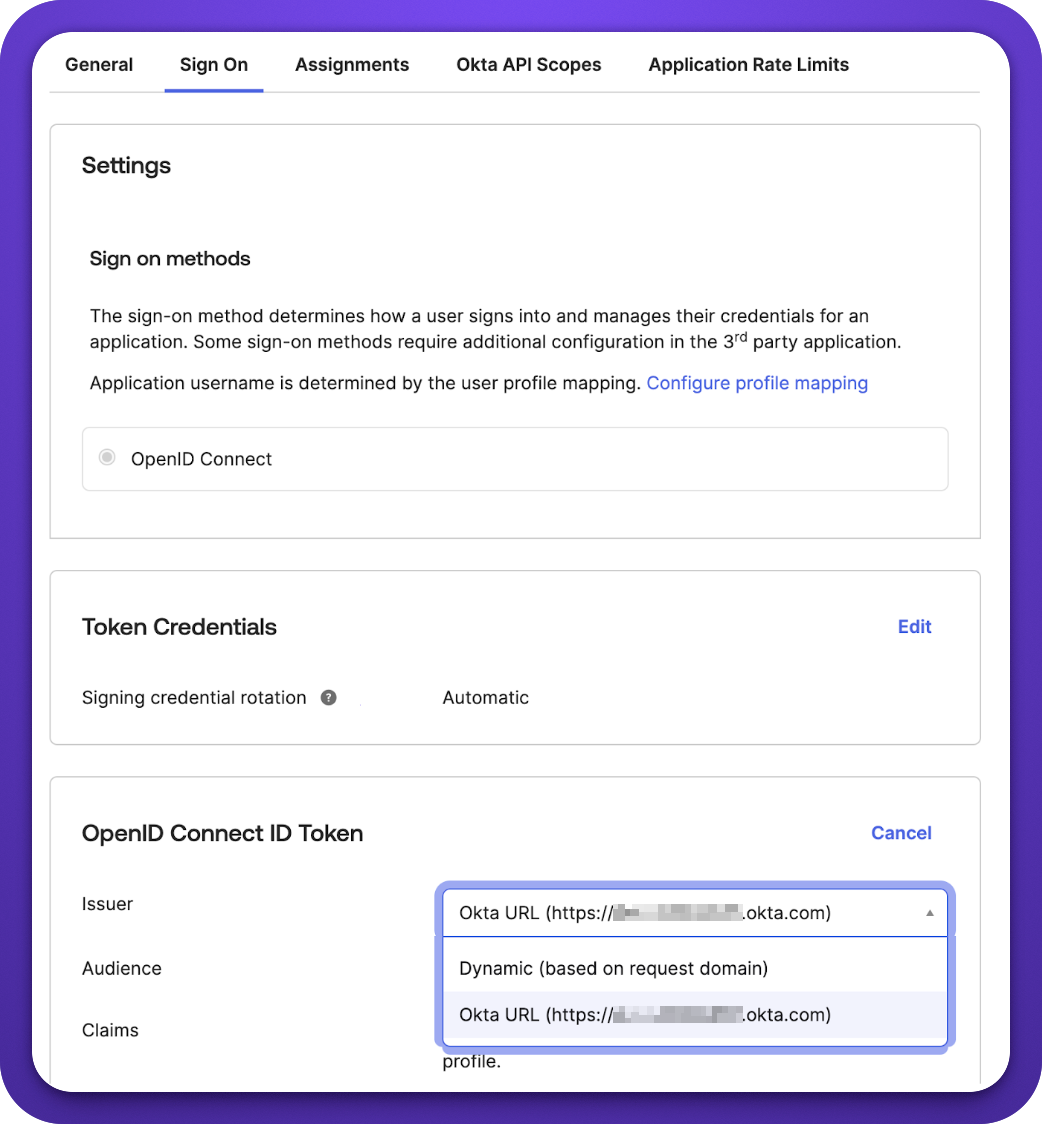
On the Sign On tab, scroll to OpenID Connect ID Token and set Issuer to a static URL (the Okta URL, not Dynamic). Copy this value.
Add the credentials to Hadrius
On the General tab, copy the Client ID and Client secret. Paste them, along with the Issuer URL from the previous step, into the Client ID, Client Secret and Okta Domain fields below.
The client secret is sensitive. Paste it directly into the form below and don't share it by email or chat.